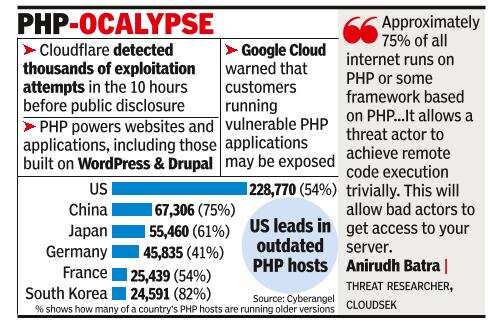
BENGALURU: It has been a difficult day for cybersecurity, with critical vulnerabilities in PHP triggering an urgent global patching effort, millions of reported hacking attempts, and precautionary shutdowns of some online services. Microsoft CEO Satya Nadella said the scale of the incident was unusual, remarking at an event in Cologne in Germany that he had not seen anything like it “in a long, long time”.The Indian Computer Emergency Response Team (CERT-In) issued a critical-severity warning over two vulnerabilities in PHP, a widely used open-source scripting language that powers websites and web applications. The flaws could allow unauthenticated attackers to execute malicious code remotely, disclose memory and potentially compromise affected systems.In its advisory issued on Wednesday, CERT-In said reports had confirmed large-scale exploitation in the wild and urged organisations and individuals using affected versions to apply security updates urgently.
CERT-In Flags Vulnerabilities
Google Cloud executives Chris Betz, chief information security officer, and Raluca Ada Popa, head of Gemini Security at Google DeepMind, said PHP and cybersecurity firm Wiz Research disclosed the two vulnerabilities after research that used multiple AI models to identify and help remediate them.Google Cloud said its own infrastructure was not vulnerable, but warned that customers running PHP applications on the platform could be exposed. It urged customers to update their applications to patched PHP versions and redeploy them. Google is also rolling out updated serverless base images for supported PHP runtimes, with automatic updates available for certain services and configurations.The scale of the response has extended beyond India. “In the 10 hours before it was publicly announced, across the network we saw thousands of attempts to exploit it,” Cloudflare CEO Matthew Prince wrote in a post on X on Wednesday. Companies and govt agencies in several countries temporarily restricted access to some online services as a precaution while they worked to secure vulnerable systems.Cloudflare’s blog said it successfully deployed mitigations for all its customers after the PHP vulnerabilities were leaked before their official disclosure date. The company observed attack traffic targeting customers and tracked how attackers modified their payloads to try to bypass its security.